

Sophisticated external attack exploited vulnerabilities in electronic approval and expense processing systems
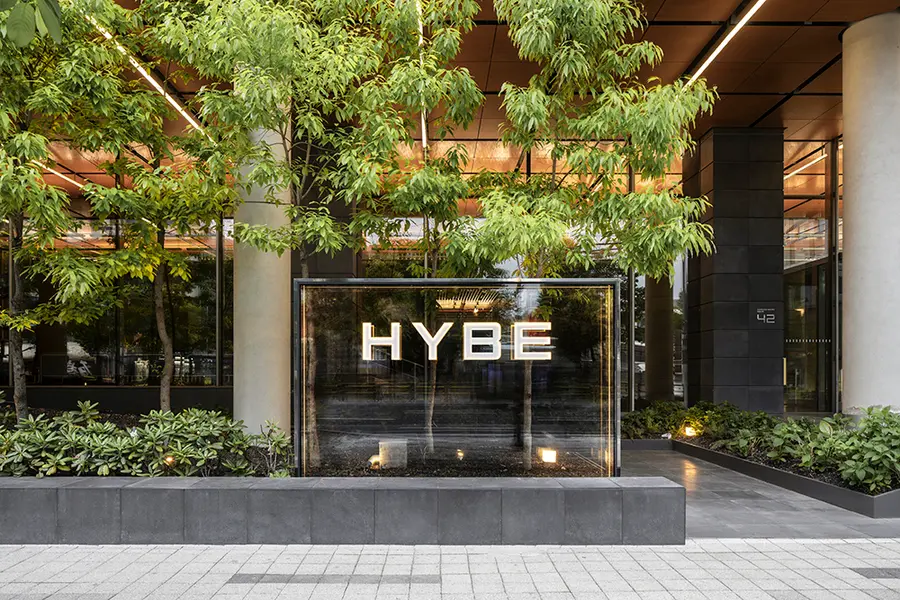
A vast amount of personal information belonging to current and former employees of HYBE (352820), South Korea's largest music agency, was found to have been leaked, the company confirmed belatedly. The breach is expected to cause widespread concern because it exposed not only basic contact details but also sensitive financial and identity information, including resident registration and passport numbers.
According to a notice HYBE posted on its website, key information about employees of partner companies and current and former staff was taken by an outside party in two incidents, on September 12–13 and October 3–5. The exposed information included names, resident registration numbers, passport numbers, bank account numbers, card numbers, mobile phone numbers, dates of birth and employee ID numbers.
The breach came to light during an internal security review. HYBE said it detected signs of unauthorized access to a document-preview solution provided by an outside vendor and integrated with its electronic approval system. A further investigation found that the same method had been used to break into the expense processing system. Some internal documents stored in the two systems—and the sensitive personal information they contained—were exposed.
Recognizing the seriousness of the incident, HYBE took urgent security measures, including blocking the IP addresses and access routes used in the attack, to prevent further exposure of information. In accordance with relevant laws, the company also completed reports to the relevant authorities, the Korea Internet & Security Agency (KISA) and the Personal Information Protection Commission.
HYBE expressed deep regret over the breach and said it would further strengthen system access controls and security monitoring. The company said it would make every effort to prevent a recurrence through a thorough investigation into the cause and fundamental improvements to its security framework.
댓글 (0)
댓글 작성
댓글을 작성하려면 로그인이 필요합니다.
로그인하기